Control automation for industrial equipment from architecture to risk control

What control automation means in industrial equipment
Control automation is the structured use of sensors, controllers, actuators, software, and operator interfaces to run industrial equipment with repeatable logic and measurable feedback. In practical terms, it is what allows a conveyor to adjust speed, a packaging line to reject faulty units, a pump skid to maintain pressure, or a robot cell to coordinate motion with upstream and downstream machines. For equipment owners, the key question is not whether automation is useful. It is how to design control automation so it improves uptime, safety, data visibility, and maintainability without creating fragile systems that are difficult to secure or support.
Industrial automation is expanding because factories need more consistent output, better energy control, faster changeovers, and more traceable operations. The International Federation of Robotics reported in its World Robotics 2026 release dated September 24, 2026, that the global operational stock of industrial robots reached about five million units in 2025, with more than 600,000 new units installed during the year. Robots are only one part of automation, but the figures point to a broader manufacturing trend: more equipment is being connected, programmed, monitored, and optimized through control systems.
For more context on related industrial technology topics, see the automation systems section.
The basic architecture of a control automation system
A control automation system is easiest to manage as a layered architecture. Each layer has its own role, timing requirement, and risk profile. Confusing those roles can quickly make a system unreliable. A high-speed motion loop, for example, should not depend on an enterprise dashboard. A maintenance report should not interfere with a safety interlock. Good architecture keeps these functions connected where needed, but not unnecessarily dependent on each other.
Field devices and physical feedback
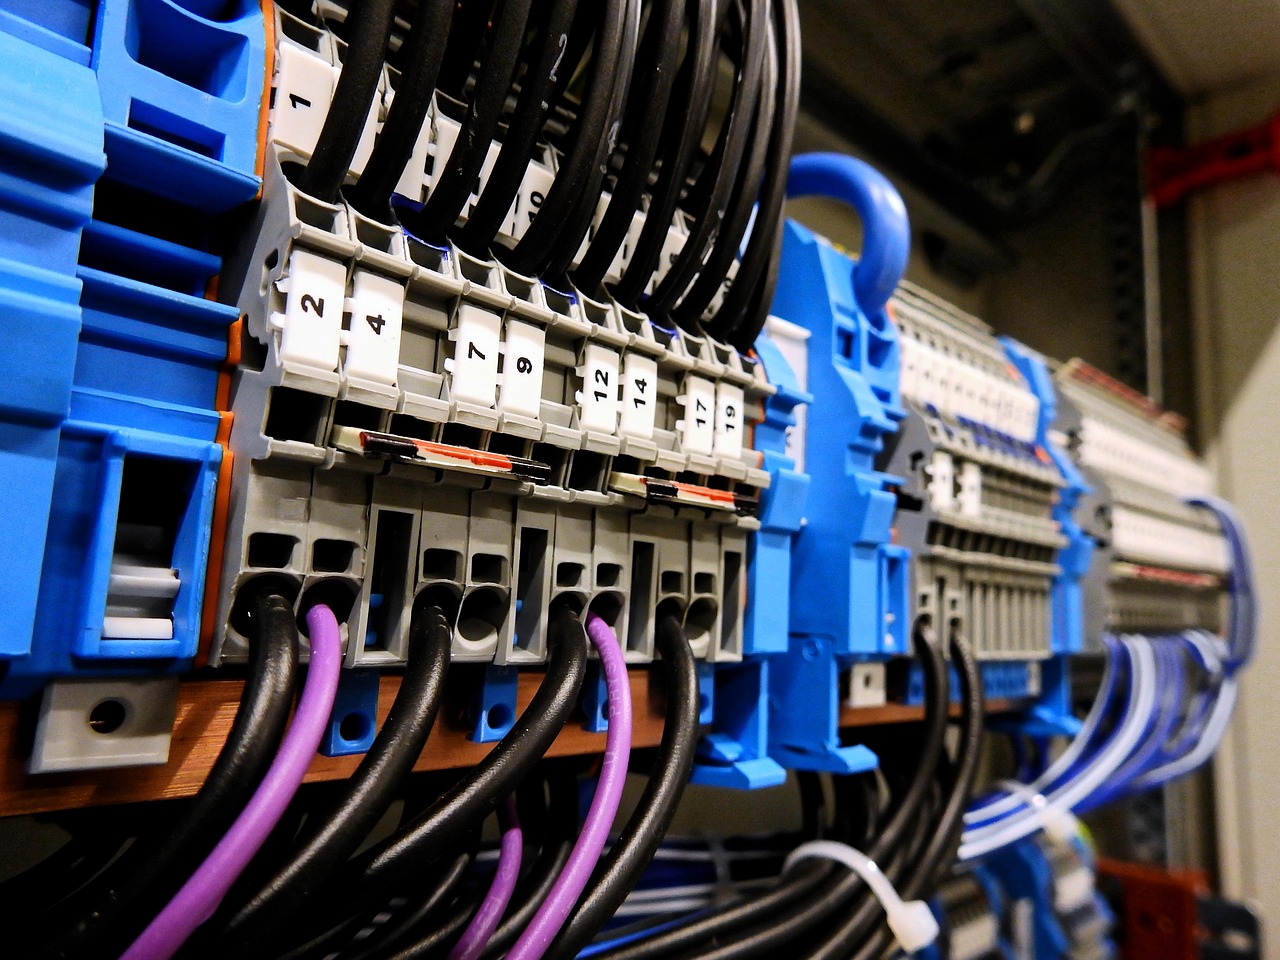
The lowest layer is the physical process. It includes motors, drives, valves, cylinders, heaters, sensors, encoders, switches, scanners, and measuring instruments. These components convert real-world conditions into signals and convert control decisions back into physical action. For equipment builders and plant teams, automation success often starts here. Poor sensor placement, electrical noise, weak enclosures, unstable air supply, or inconsistent calibration can make even well-written control logic appear unreliable.
Designers should define what must be measured, how fast it must be measured, how accurate the measurement must be, and what should happen when a value is missing or implausible. A temperature loop, a servo axis, and a presence sensor on a conveyor may all feed the same control system, but they have very different response-time and diagnostic requirements.
Controllers and machine logic
The controller layer typically includes PLCs, PACs, industrial PCs, motion controllers, safety controllers, and distributed I/O. This layer executes machine logic, sequencing, interlocking, and closed-loop control. In many industrial applications, deterministic behavior matters more than raw computing power. The controller must react predictably during normal operation, startup, shutdown, fault recovery, and manual intervention.
Good control automation logic is more than a collection of inputs and outputs. It should include clear operating modes, permissives, alarms, diagnostics, fault handling, and recovery states. A common mistake is to automate the ideal production sequence while underdesigning abnormal states. Operators and maintenance technicians spend much of their time dealing with jams, changeovers, sensor faults, and upstream delays. If the control program does not handle these conditions clearly, the system will be harder to run and support than it should be.
HMI, SCADA and production systems
The operator and supervisory layer includes HMI panels, SCADA systems, historians, recipe systems, and sometimes connections to MES or ERP platforms. This layer helps people see what the equipment is doing, change authorized parameters, review alarms, and analyze performance. It is also where industrial equipment increasingly becomes part of a wider data environment.
The design issue is separation of purpose. Operators need fast, clear, and reliable screens for current production. Engineers may need trend data and alarm history. Managers may need production summaries. Cybersecurity teams may need asset information and event visibility. A single automation project may serve all of these users, but the system should not overload operators with management dashboards or expose critical control functions to unnecessary network access.
Why the control layer is changing
Traditional control systems were often designed as isolated machine islands, and many still run that way. At the same time, industrial equipment is increasingly expected to exchange data with other systems. Production teams want OEE signals, downtime reasons, batch records, energy data, and quality traceability. Maintenance teams want condition monitoring and remote diagnostics. Corporate teams want standardized data models and cybersecurity governance.
This does not mean every machine needs a complex cloud architecture. In many cases, a simple, well-documented data path from a PLC to an HMI, historian, or edge gateway is more valuable than a broad platform rollout. The most useful control automation projects identify which data supports a real decision. Speed, temperature, pressure, cycle count, alarm frequency, reject rate, and energy consumption can be valuable signals when they are accurate, time-stamped, and connected to a practical workflow.
Cybersecurity is another major reason the control layer is changing. NIST Special Publication 800-82 Revision 3, published in September 2023, describes operational technology as systems and devices that interact with the physical environment and emphasizes that OT security must account for performance, reliability, and safety requirements. That distinction matters. Industrial control systems cannot be treated exactly like office IT systems because downtime, latency, and uncontrolled patching can create physical consequences.
The ISA/IEC 62443 series also reflects this shift. The International Society of Automation describes the series as a framework for electronically secure industrial automation and control systems, with responsibility shared among asset owners, product suppliers, system integrators, and service providers. In other words, secure control automation is not only a firewall decision. It is a lifecycle issue involving design, procurement, configuration, operations, maintenance, and upgrades.
Practical design priorities for control automation projects
A control automation project should start with operational intent, not with a hardware list. Hardware and software choices matter, but they should follow a clear definition of the process, performance target, safety need, data requirement, and maintenance model. The following priorities help keep projects grounded.
Define the operating outcome first
Before selecting a controller platform or network, define what the equipment must achieve. Is the main target higher throughput, better repeatability, lower scrap, safer operation, less manual adjustment, faster changeover, or better traceability? A system designed for high-speed packaging may prioritize motion synchronization and jam recovery. A water treatment skid may prioritize stable process control, alarm management, and remote monitoring. A robotic loading cell may prioritize safety zones, part presentation, and fault recovery.
When outcomes are specific, the automation design can be tested against them. When outcomes are vague, the project tends to become a technology installation rather than a process improvement.
Build safety and cybersecurity into the lifecycle
Safety and cybersecurity should not be added at the end of a project. Safety functions need risk assessment, defined performance requirements, validation, and documentation. Cybersecurity needs asset identification, network segmentation, access control, backup planning, patch strategy, and incident response procedures. These activities affect the architecture, not only the documentation package. See also: production equipment.
NIST Cybersecurity Framework 2.0, published on February 26, 2024, is not specific to industrial control systems, but it is useful as a governance reference because it organizes cybersecurity outcomes without prescribing a single implementation method. For industrial automation teams, that approach is practical: a small machine builder, a process plant, and a multi-site manufacturer may need different controls, but each still needs a way to identify, protect, detect, respond, and recover.
Design for maintainability
Many automation failures are not caused by poor technology. They are caused by systems that are hard to understand after the project team leaves. Maintainability should be a formal design requirement. That means consistent tag naming, readable code structure, documented operating modes, clear electrical drawings, backed-up controller programs, spare parts lists, and alarm messages that tell operators what to do.
Remote access also needs careful planning. It can reduce downtime when specialists can diagnose a fault quickly, but it should be controlled through approved access methods, authentication, logging, and time-limited permissions. Convenience should not become a permanent open path into the control network.
Common risks in control automation and how to reduce them
Control automation creates value when it reduces variability and gives people better control of the process. It creates risk when it hides complexity, concentrates failure points, or connects systems without governance. The table below summarizes common risks and practical mitigations.
| Risk | How it appears | Practical mitigation |
|---|---|---|
| Unclear control scope | Teams disagree on whether a function belongs in the PLC, HMI, SCADA, or MES | Create a control narrative and responsibility matrix before programming begins |
| Poor alarm design | Operators receive too many alarms or alarms without useful instructions | Prioritize alarms, remove duplicates, and write messages that describe cause and action |
| Weak data quality | Dashboards show numbers that operators do not trust | Validate sensors, timestamps, units, sampling rates, and calculation logic |
| Network exposure | Control devices are reachable from unnecessary systems or users | Use segmentation, controlled access, account management, and documented remote support procedures |
| Vendor lock-in without planning | Future upgrades become expensive or difficult because interfaces are closed or undocumented | Define integration requirements, export needs, and lifecycle support expectations during procurement |
| Insufficient backup and recovery | A failed controller or HMI causes long downtime because the latest program is unavailable | Maintain tested backups, version control, and recovery procedures for controllers, drives, HMIs, and industrial PCs |
The table also shows why automation should be reviewed as a system, not as a collection of devices. A high-quality PLC cannot compensate for a weak alarm philosophy. A modern HMI cannot fix inaccurate field signals. A cybersecurity policy has limited value if remote access paths are undocumented. The strength of the system depends on the connections among design choices.
A phased roadmap for implementation
For existing industrial equipment, the safest modernization path is often phased. A full replacement may be justified for obsolete controls or major capacity changes, but many facilities can reduce risk by separating assessment, stabilization, integration, and optimization.
- Assess the current state. List controllers, networks, HMIs, drives, sensors, safety systems, software versions, spare parts, and known failure points. Identify unsupported hardware and missing backups.
- Define operational priorities. Rank the problems that matter most: downtime, quality loss, manual adjustment, safety exposure, slow changeover, energy use, or lack of production visibility.
- Stabilize the control base. Correct unreliable signals, electrical issues, missing documentation, and unclear fault recovery before adding advanced analytics or new supervisory layers.
- Segment and document networks. Separate control functions from nonessential traffic and document how data moves between machines, servers, engineering workstations, and business systems.
- Add useful data connections. Start with data that supports decisions, such as downtime reason codes, cycle times, alarm frequency, reject counts, or energy consumption.
- Validate and train. Test normal and abnormal states, then train operators and maintenance teams on the actual screens, alarms, manual modes, and recovery procedures.
- Review lifecycle needs. Establish a routine for backups, software updates, cybersecurity reviews, spare parts, change control, and documentation updates.
This roadmap is deliberately practical. It avoids the assumption that every facility needs the same level of digital maturity. A small packaging line and a large process plant may both need control automation, but the right scope, risk tolerance, and support model will differ.
How to evaluate whether a system is ready for modernization
An industrial equipment team should consider modernization when the existing control system limits operations or creates unacceptable risk. Warning signs include obsolete controllers, unavailable spare parts, undocumented programs, frequent unexplained stoppages, excessive manual workarounds, poor alarm visibility, unreliable production data, or remote access practices that no one can fully explain.
Modernization does not always mean replacing everything. Sometimes the highest-value step is improving documentation, backing up programs, upgrading an HMI, replacing a failing network switch, adding a historian, or segmenting the control network. In other cases, a complete controls retrofit is justified because the system cannot meet safety, capacity, or support requirements.
The strongest business case connects technical changes to operational outcomes. Instead of saying a machine needs a new PLC, the case should explain what the new control platform enables: shorter downtime, clearer diagnostics, safer maintenance access, better recipe control, improved data collection, or longer support life. That framing helps operations, engineering, maintenance, and management make decisions using the same language.
Frequently asked questions
Is control automation the same as industrial automation?
Control automation is a core part of industrial automation, but it is not the whole category. It focuses on the control layer that senses conditions, executes logic, and commands equipment. Industrial automation can also include robotics, production software, data platforms, material handling, inspection systems, and enterprise integration.
What is the difference between PLC, SCADA and HMI?
A PLC usually executes machine or process logic in real time. An HMI gives operators a local interface to view status, change permitted settings, and respond to alarms. SCADA supervises wider processes, often across multiple machines, areas, or sites, and may include trending, alarming, reporting, and historian functions.
Why is cybersecurity important for control automation?
Control systems interact with physical equipment. A cybersecurity problem can therefore affect production, safety, quality, or environmental controls, not just data confidentiality. That is why OT security guidance emphasizes reliability, controlled change, segmentation, access management, and recovery planning.
What should be documented before an automation upgrade?
At minimum, teams should document equipment functions, I/O lists, network architecture, controller programs, HMI applications, safety functions, alarm lists, software versions, backup locations, remote access methods, and known operational problems. Better documentation reduces project risk and makes future troubleshooting easier.