System automation for industrial equipment integration and OT security
What system automation covers in industrial equipment
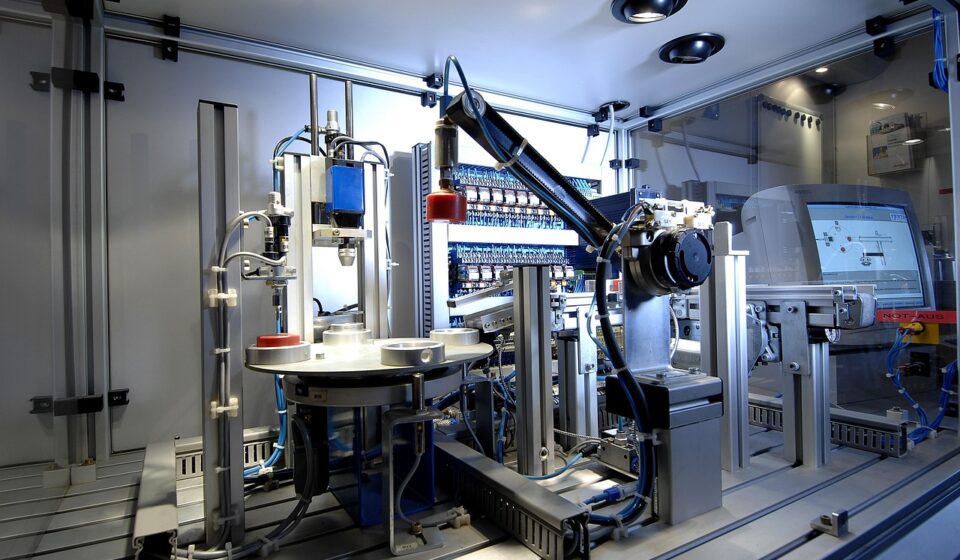
System automation is the coordinated use of control hardware, software, sensors, actuators, networks, and data systems to run industrial equipment with less manual intervention and more predictable performance. In a modern plant, it is not limited to one robot, PLC, conveyor, pump, or packaging cell. It describes how equipment, production workflows, alarms, quality checks, maintenance signals, and business systems work together as a connected operating environment.
For industrial equipment teams, the practical goals are usually straightforward: reduce avoidable variation, improve uptime, make operations easier to monitor, and support safer decisions. The difficulty is that automation projects often underperform when they are treated as isolated control upgrades. A new controller may improve one machine, but it will not by itself solve scheduling gaps, poor data quality, spare-parts issues, or cybersecurity exposure.
This is why system automation belongs within a broader automation systems strategy. Strong projects connect engineering requirements with operations, maintenance, IT, safety, and management needs before equipment is specified or software is configured.
The architecture behind a connected automation system
A useful way to understand system automation is to separate the layers that must work together. Each layer has a different role, different failure modes, and different owners. When these layers are blurred, teams can end up with overloaded PLCs, duplicate databases, unreliable dashboards, or control networks that are too exposed to enterprise traffic.
| Layer | Main role | Typical components | Key planning question |
|---|---|---|---|
| Field level | Detect and act on physical conditions | Sensors, actuators, drives, valves, instruments | Are measurements accurate, maintainable, and suitable for the environment? |
| Control level | Execute real-time machine or process logic | PLCs, DCS controllers, safety controllers, motion control | Can the control system meet timing, safety, and reliability requirements? |
| Supervisory level | Monitor operations and support operator decisions | HMI, SCADA, alarms, historian interfaces | Do operators receive useful context rather than alarm noise? |
| Operations management level | Coordinate production, quality, and maintenance workflows | MES, batch records, OEE tools, quality systems | Does production data match how the plant actually runs? |
| Enterprise level | Plan resources, orders, inventory, and reporting | ERP, supply chain systems, analytics platforms | Which data must move between business systems and production systems? |
This layered view is more than documentation. It helps teams decide where each function should live. A fast interlock, for example, should remain close to the control layer, while a production schedule belongs in an operations or enterprise system. A quality hold may need both: immediate equipment status from the control layer and lot or batch context from higher-level systems.
Integration standards and why ISA-95 still matters
One of the hardest parts of system automation is not installing devices. It is making different systems exchange the right information consistently. Industrial sites often run a mix of legacy machines, vendor-specific controllers, SCADA platforms, databases, spreadsheets, and ERP modules. Without a common model, integration can turn into a set of custom point-to-point links that are difficult to maintain.
The ISA-95 standard, also published internationally as IEC 62264, remains important because it gives manufacturers a structured way to think about information exchange between business systems and manufacturing control functions. The International Society of Automation describes ISA-95 as an abstract model for information exchange among manufacturing control functions and enterprise business functions. In practice, it helps teams define objects such as equipment, materials, personnel, production schedules, production performance, and quality data.
For equipment owners, the value is practical. If a packaging line reports downtime, the system should make clear whether the event is a machine fault, material shortage, changeover delay, quality hold, or operator stop. If a batch is released, higher-level systems need traceable context rather than a simple finished or not finished signal. ISA-95 does not remove the need for engineering judgment, but it reduces ambiguity in system boundaries and data definitions.
A good integration plan should answer four questions before development begins:
- Which system is the source of truth for each data object?
- Which events must be exchanged in real time, near real time, or by scheduled batch transfer?
- How will data quality, missing values, and rejected transactions be handled?
- Who owns changes when equipment logic, production workflows, or ERP fields are modified?
These questions are not glamorous, but they prevent many automation projects from becoming fragile after commissioning.
Cybersecurity and resilience now shape automation design
Industrial automation used to be designed mainly around safety, uptime, process performance, and maintainability. Those priorities still matter, but cybersecurity and operational resilience now need to be considered early in the design phase. This is especially important as plants connect equipment to historians, remote support tools, cloud services, analytics platforms, and enterprise networks.
NIST Cybersecurity Framework 2.0, published in 2024, broadened the framework so it can be used by organizations of all sizes and sectors. For industrial environments, its emphasis on governance is significant because cybersecurity decisions in automation cannot sit only with IT or only with controls engineering. Risk ownership, supplier access, asset inventory, backup strategy, incident response, and recovery objectives all cross departmental lines.
NIST also released an initial public draft of SP 800-82 Revision 4 on September 21, 2026, with comments open through November 30, 2026. The draft focuses on operational technology security and reflects topics that automation teams now face more often, including Industrial Internet of Things, cloud convergence, asset management, network monitoring, and zero trust principles. Because it is a draft, it should not be treated as final guidance, but it does indicate the direction of current OT security thinking.
ISA/IEC 62443 is another important reference point for industrial automation and control system security. The series addresses security across people, processes, and technology, including risk assessment, system design, and secure development practices. For automation projects, its most useful message is that security cannot be bolted on after acceptance testing. It needs to be reflected in architecture, zones and conduits, user access, supplier responsibilities, patch planning, and lifecycle management.
From an equipment perspective, resilience means asking what happens when something fails. Can operators continue safely if the MES is unavailable? Can production restart from a known good state after a controller replacement? Are backups tested, or only stored? Are remote access sessions logged and approved? A system automation project that improves throughput but leaves recovery unclear may increase business risk rather than reduce it.
AI, analytics, and autonomy need disciplined data foundations
AI and advanced analytics are becoming more visible in industrial automation, but they do not replace basic system discipline. A vendor-sponsored Rockwell Automation 2025 smart manufacturing survey reported responses from 1,560 leaders across 17 manufacturing countries and highlighted strong interest in AI, cybersecurity, and smart manufacturing investments. Surveys like this are useful indicators of industry direction, but they should be read as market research rather than universal proof of plant-level results. See also: production equipment.
The practical value of analytics usually depends on data foundations that are less visible but more important. Equipment tags need consistent names. Time stamps need to align. Alarm states need clear definitions. Maintenance events need accurate cause codes. Production counts need to distinguish good units, scrap, rework, and test cycles. Without this foundation, dashboards may look modern while still giving misleading signals.
In system automation, AI use cases can be grouped into three practical categories:
- Decision support, such as anomaly detection, energy analysis, quality prediction, or maintenance prioritization.
- Workflow automation, such as routing alerts to the right technician or creating suggested work orders from equipment conditions.
- Closed-loop optimization, where approved models influence setpoints, scheduling, or process adjustments under defined constraints.
The third category requires the most caution. Closed-loop automation can create real value, but only when process limits, safety controls, model validation, fallback states, and operator authority are clearly defined. In many plants, the better first step is not full autonomy but reliable visibility: fewer manual logs, better downtime classification, cleaner alarm priorities, and trusted production data.
A practical planning checklist for automation projects
System automation succeeds when technical design and operational reality are aligned. Before selecting equipment or software, project teams should create a simple but rigorous plan that connects business outcomes with engineering requirements.
- Define the operational problem. Avoid vague goals such as digital transformation. State the target in concrete terms, such as reducing unplanned downtime on a filling line, improving traceability for regulated batches, or shortening changeover confirmation time.
- Map the current process. Include manual workarounds, spreadsheets, operator decisions, maintenance calls, rework loops, and approval steps. Hidden workflows often determine whether automation will be adopted.
- Inventory assets and data sources. List controllers, HMIs, historians, networks, instruments, databases, and software versions. Asset visibility is also a cybersecurity requirement, not only an engineering convenience.
- Set integration boundaries. Decide what belongs in PLC logic, SCADA, MES, ERP, analytics platforms, and manual procedures. Do not push business logic into controllers simply because it is possible.
- Design for abnormal conditions. Include startup, shutdown, communication loss, sensor failure, rejected transactions, cybersecurity incidents, and recovery from backup.
- Validate with users. Operators, maintenance technicians, quality teams, and supervisors should review screens, alarm priorities, reports, and procedures before commissioning.
- Plan lifecycle ownership. Define who approves changes, tests backups, reviews user access, updates documentation, and maintains integration mappings after go-live.
This checklist is intentionally cross-functional. Automation is not only a controls task, and it is not only an IT task. It is an operating model that depends on equipment behavior, software architecture, human decisions, and risk management working together.
Common limits and trade-offs
System automation can deliver major improvements, but it also introduces trade-offs. More connectivity can improve visibility while increasing the need for network segmentation and access control. More data can support analytics while creating storage, context, and governance challenges. More automated decisions can reduce response time while making validation and accountability more complex.
Legacy equipment adds another constraint. Older machines may lack modern communication interfaces, spare capacity, or vendor support. In these cases, the right answer may be phased modernization rather than full replacement. Edge gateways, protocol converters, separate monitoring sensors, or historian upgrades can provide useful visibility, but they should be evaluated carefully for security, maintainability, and data accuracy.
There is also a people dimension. If operators do not trust automated instructions, they will bypass them. If maintenance teams cannot interpret diagnostic data, alarms become noise. If management only measures headline output, teams may ignore quality losses or recovery risks. Effective automation projects treat training, documentation, and change management as core deliverables.
Frequently asked questions
Is system automation the same as factory automation?
They overlap, but they are not identical. Factory automation often refers to automating production tasks on the shop floor. System automation is broader because it includes how equipment, control systems, operations software, data flows, security practices, and business systems work together.
What is the first step in an industrial system automation project?
The first step is defining the operational problem and mapping the current process. Technology selection should come later. Without a clear process map, teams may automate the wrong workflow or create integrations that do not match real plant behavior.
Why is OT security important for automation systems?
OT security matters because automation systems interact with physical equipment, production quality, safety functions, and uptime. A cybersecurity incident in an industrial environment can affect operations, recovery time, and physical processes, not only business data.
Can AI improve system automation?
Yes, but AI depends on reliable data, clear constraints, and validated workflows. The strongest near-term uses are often decision support, anomaly detection, maintenance prioritization, and quality analysis. Closed-loop AI control requires more rigorous testing and governance.
How should companies measure automation success?
Success should be measured against the original operational goal. Useful metrics may include uptime, scrap, changeover time, alarm response, energy use, maintenance efficiency, traceability, recovery time, and user adoption. A project can look successful technically but still fail if it does not improve daily operations.